Sunny Chokshi

Blog

I am a PhD student testing how well open LLMs review code for security bugs. Each post covers one result from my own experiments, such as why a model that flags every snippet looks best on detection rate, or how a hex key size set off false alarms. Every post links to the preprint and dataset on Zenodo, so you can check the numbers and reuse the data.
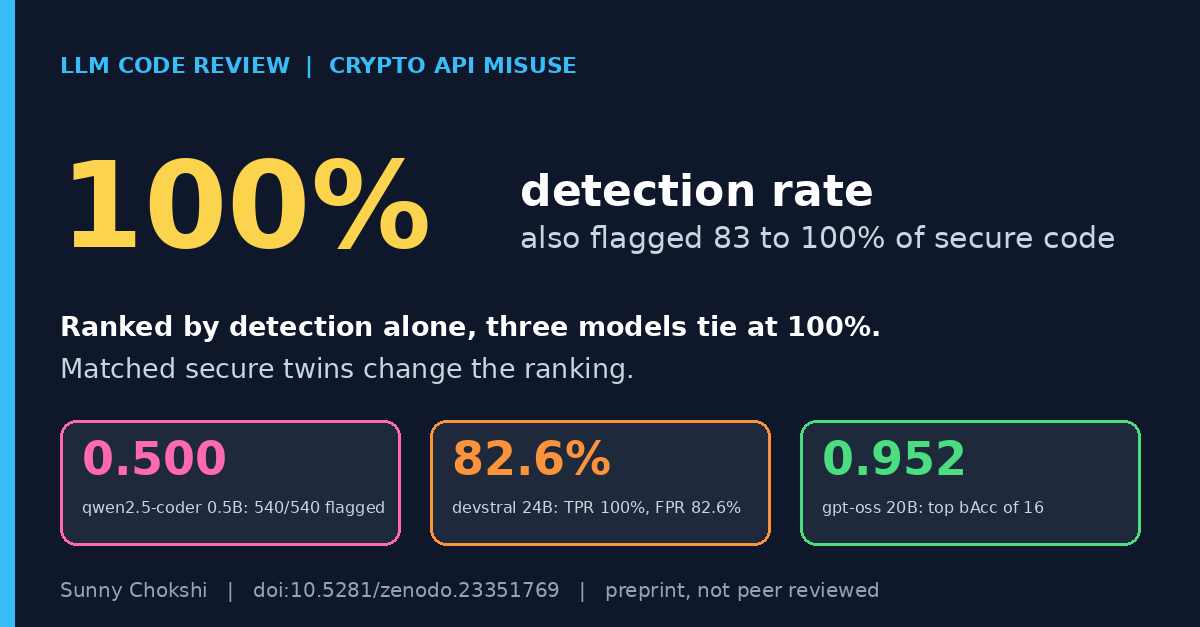
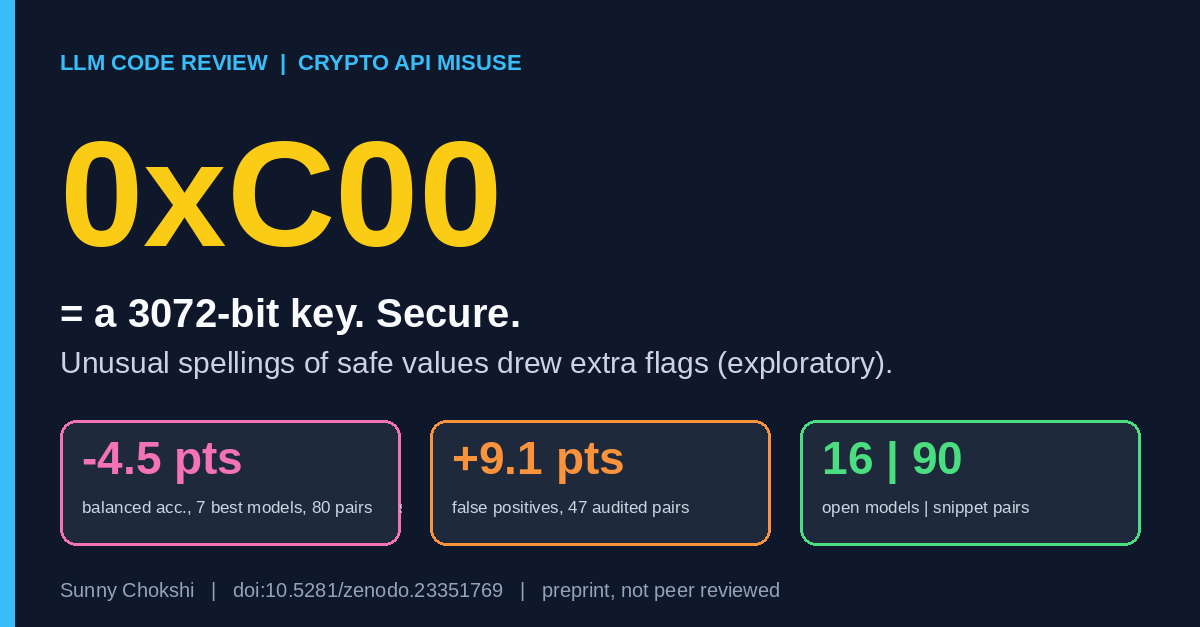
Detection rate alone ranks the worst LLM code reviewers firstOctober 28, 2026Detection rate alone ranks the worst LLM code reviewers firstLLM vulnerability detectionLLM code reviewerfalse positive ratebalanced accuracycryptographic API misuse detectionRead the post →A hex literal made LLM code reviewers raise false alarmsOctober 28, 2026A hex literal made LLM code reviewers raise false alarmscryptographic API misuse detectionLLM code reviewLLM false positivessecure code reviewhex literal key sizeRead the post →