Blog
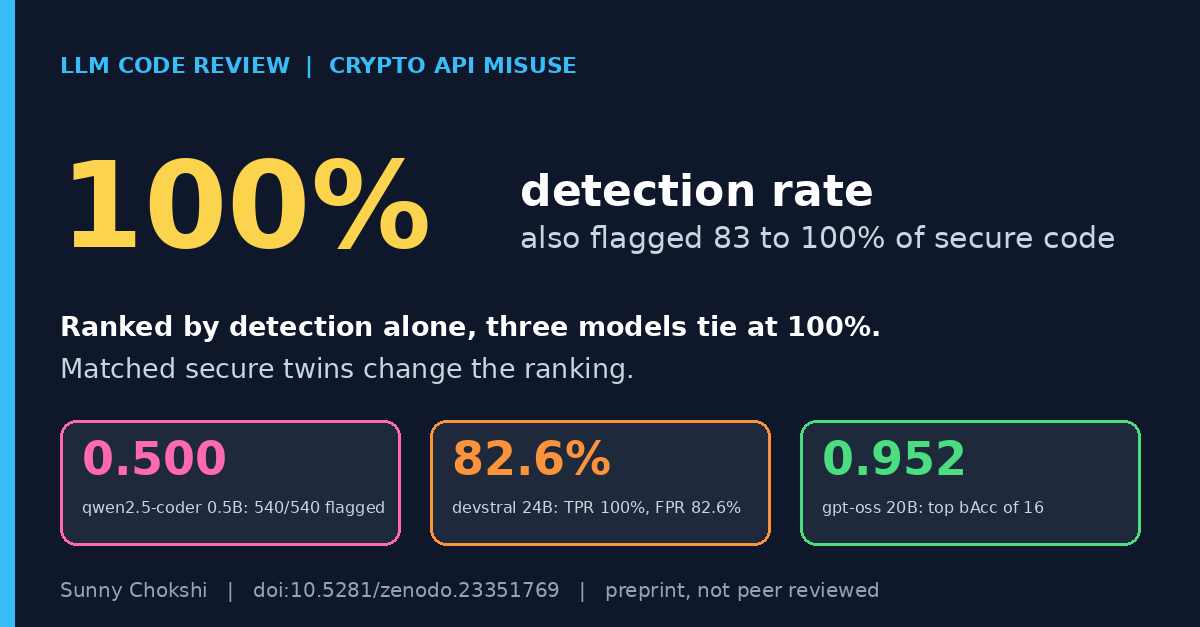
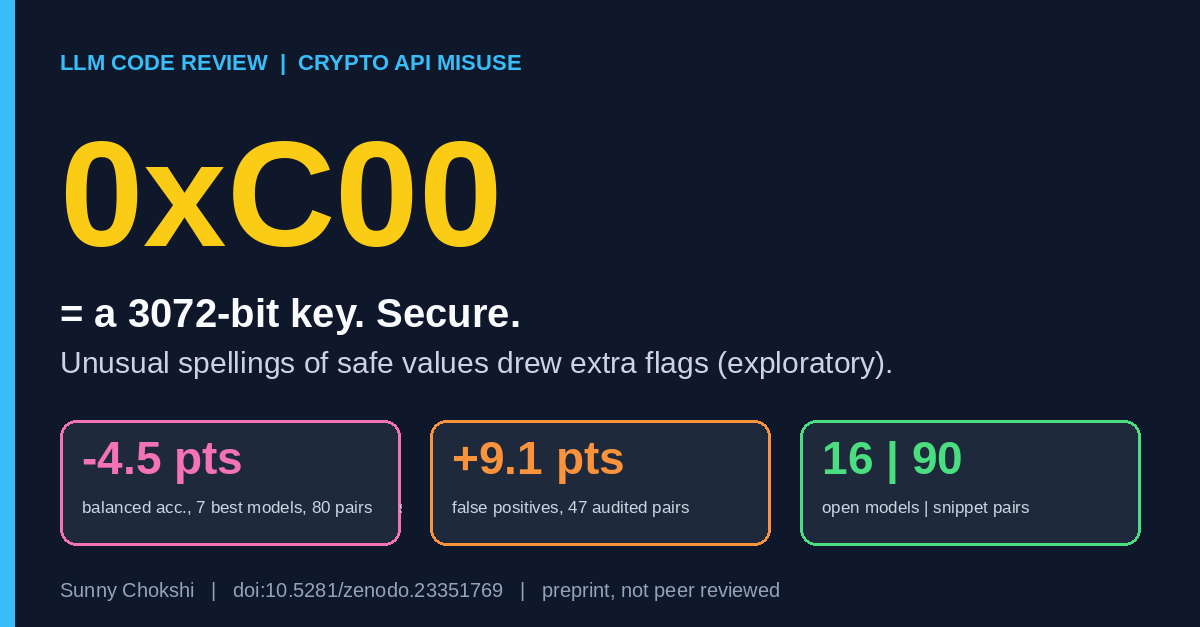
I am a PhD student testing how well open LLMs review code for security bugs. Each post covers one result from my own experiments, such as why a model that flags every snippet looks best on detection rate, or how a hex key size set off false alarms. Every post links to the preprint and dataset on Zenodo, so you can check the numbers and reuse the data.